Labels

Lifestyle (484) Investing (417) Entertainment (317) Singapore (270) Technology (152) Insights (144) Rewards (137) Gaming (111) Equities (97) Data (93) AI (92) Food (90) U.S. (77) Sports (76) Crypto (74) Travel (69) Portfolio (55) News (54) Credit Card (38) Earnings (37) Football (36) Movies (36) Savings (34) Property (30) Policies (27) Tennis (27) Shows (24) Holidays (23) Promotions (20) Malaysia (18) Toys (18) Bonds (16) World (15) REITs (14) T-Bills (13) Apps (11) China (11) Currency (10) Healthcare (10) Referral (10) Retirement (9) Anime (8) DeFi (8) CPF (7) Cash Management (7) ETFs (6) Security (6) Miles (5) Shopping (5) Commodities (4) Japan (4) Robotics (4) Weird (4) platform (4) Cashback (3) Insurance (3) 1-For-1 (2) Blog (2) Reviews (2) Robo-Advisor (2) Asia (1) Australia (1) Banking (1) Funds Management (1) Futuristic (1) Government (1) Indonesia (1) Inflation (1) Interesting (1) Nerfs (1) SGD (1) SSB (1) Social (1) Thailand (1)
Showing posts with label Crypto. Show all posts

Monday, 16 November 2026

Crypto Updates: Trezor Confirms Hidden Implants in CryptoBilis-Sold Wallets That Can Steal Recovery Phrases

Source:


ChatGPT:

Trezor Confirms Hidden Hardware Implants in Crypto Wallets – Article Summary & Social Sentiment

Article: The Hacker News
Published: 13 November 2026
Topic: Cryptocurrency security, hardware wallet tampering and supply-chain attacks
Overall assessment: Serious cybersecurity incident with potentially significant implications for cryptocurrency investors.

1. Article Summary

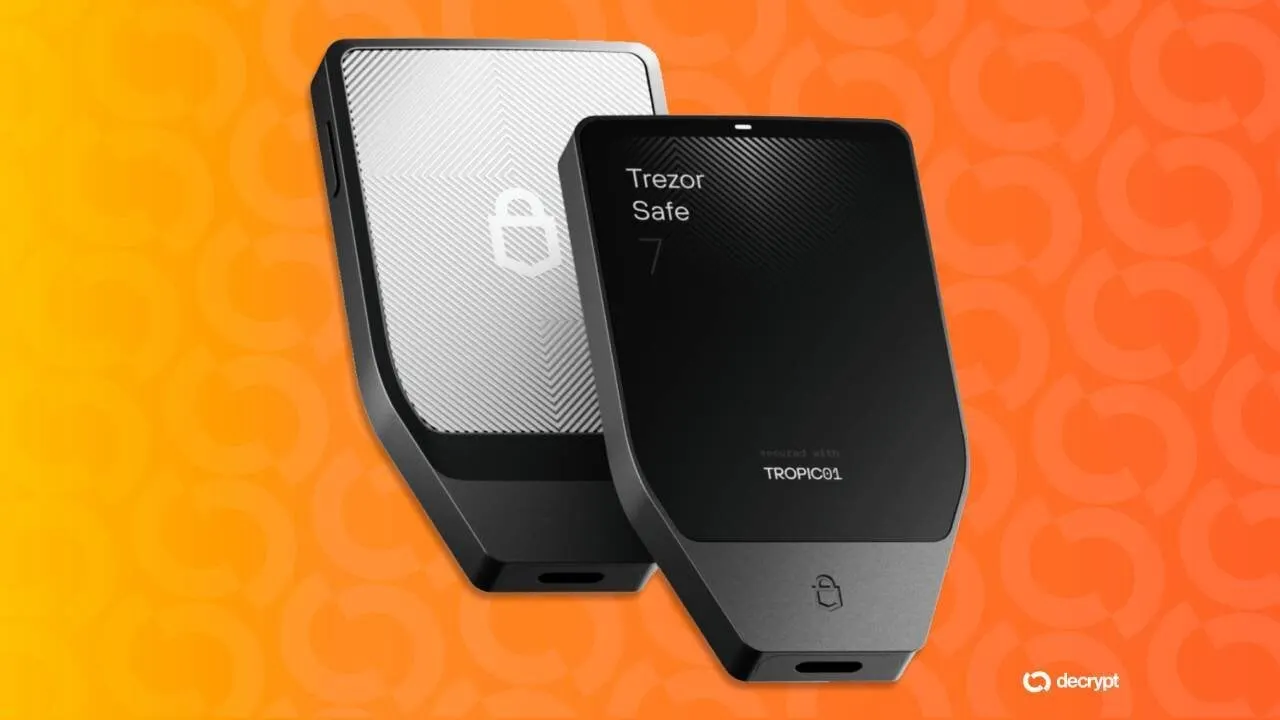
The article reports that Trezor has confirmed that three of its Safe 5 hardware wallets contained malicious hardware implants.

The affected devices were sold through an authorised Southeast Asian reseller called CryptoBilis.

What happened?

Attackers secretly installed an additional circuit board inside genuine Trezor Safe 5 devices.

The malicious component:

  • Was installed between the wallet's main circuit board and screen.
  • Could read information displayed on the device.
  • Captured users' cryptocurrency recovery phrases (seed phrases).
  • Also captured passphrases displayed on the screen.
  • Transmitted the stolen information through a cellular network to an attacker-controlled server.
  • Could store captured information and transmit it later if connectivity was unavailable.

The worrying part is that the implant did not modify the original device firmware or interfere with its Secure Element.

This means the device could appear to function normally.

How many devices were affected?

Trezor confirmed:

ItemFindings
Confirmed compromised devices3
Affected modelTrezor Safe 5
ResellerCryptoBilis
Purchase period20 August – 23 September 2026
Customers who contacted Trezor48
Confirmed financial lossesNone reported
Other resellers affectedNo confirmed cases

The investigation is ongoing.

What has Trezor done?

Trezor has taken several measures:

  1. Released firmware version 2.13.1 on 11 November 2026 to block the identified implants.
  2. Reduced its authorised reseller network by approximately 80%.
  3. Introduced stricter supply-chain security requirements.
  4. Offered replacement devices to affected CryptoBilis customers.
  5. Continued investigating potentially compromised devices.

Important: Installing the firmware update does not reverse a recovery phrase that may already have been stolen.

Affected customers must create a completely new wallet with a new recovery phrase and transfer their funds.

Sources: The Hacker News original article | Trezor official investigation update (12 November)


2. Social Media & Forum Sentiment

I examined available discussions and search results across cryptocurrency communities, Reddit, X and other online platforms.

The discussion is particularly interesting because this incident follows a similar hardware implant incident involving Ledger wallets sold through the same reseller.

A. Reddit – Strong discussion and security concerns

Reddit has some of the most substantive discussions surrounding this incident.

Relevant discussions:

Some notable reactions:

Reaction 1: Concern about hardware wallet security

A Reddit user commented:

Give feedback

Main discussion themes:

  • Hardware wallets are not necessarily safe if their supply chains are compromised.
  • Firmware updates cannot recover previously stolen seed phrases.
  • Some users are reconsidering their trust in hardware wallet manufacturers.
  • Discussions about multisignature wallets and alternative cold-storage solutions.
  • Greater emphasis on purchasing directly from manufacturers.

My assessment: Negative sentiment, with considerable concern about the security assumptions behind hardware wallets.

B. X (Twitter)

Trezor has published official updates about its investigation.

The main discussion revolves around:

  • The discovery of three compromised devices.
  • The firmware update.
  • The relationship between CryptoBilis and the earlier Ledger incident.
  • The reduction of authorised resellers.

Trezor's official announcement is available through its investigation update.

Trezor official announcement

Sentiment: Negative towards the incident, but some appreciation for Trezor's transparency and response.

C. HardwareZone

I could not identify a substantial, directly relevant HardwareZone discussion specifically about the November 13 Trezor confirmation.

However, the incident is particularly relevant to Singapore because the Singapore Police Force previously issued an advisory about malicious hardware components found in Ledger wallets sold through certain retail outlets.

This makes the issue more than an overseas cryptocurrency security story.

D. Facebook

I could not establish a substantial public Facebook discussion specifically about this latest Trezor confirmation.

Potential discussion areas include:

  • Cryptocurrency wallet safety.
  • Whether hardware wallets remain trustworthy.
  • Buying cryptocurrency hardware from authorised retailers.
  • Risks associated with compromised supply chains.

E. Instagram

No substantial, independently verifiable Instagram discussion specifically about the November 13 announcement surfaced in my research.

F. TikTok

No significant directly relevant TikTok discussion could be independently verified.

The incident nevertheless has potential for cryptocurrency security awareness content, particularly explaining why hardware wallets can be compromised even when they are genuine products.

G. Threads

No substantial, independently verifiable Threads discussion specifically about this announcement surfaced.

Social Media Discussion Summary

PlatformDiscussion levelGeneral sentiment
RedditHighNegative
XModerateNegative
HardwareZoneLow / not verifiedUnclear
FacebookLow / not verifiedUnclear
InstagramLow / not verifiedUnclear
TikTokLow / not verifiedUnclear
ThreadsLow / not verifiedUnclear

Important: Low discussion levels do not necessarily mean positive sentiment. Some platforms restrict access to public discussions, and search results may not capture private groups or individual posts.


3. Singapore Implications

This incident deserves additional attention in Singapore.

The reason is that the CryptoBilis case is connected to a broader Southeast Asian supply-chain security problem.

The Singapore Police Force issued an advisory on 28 October 2026 concerning malicious hardware components discovered in Ledger wallets purchased from certain retail stores in Singapore.

There were at least two reported cases.

The Trezor incident demonstrates that this problem is not necessarily restricted to one hardware wallet manufacturer.

Sources: The Hacker News

Why this matters to cryptocurrency investors

Traditionally, hardware wallets are considered safer because private keys are stored offline.

However, this incident demonstrates three important weaknesses:

  1. Supply-chain vulnerabilities: Genuine products can be physically modified before reaching customers.
  2. Hardware-level attacks: Security checks focusing on firmware may not detect additional malicious components.
  3. Recovery phrase exposure: Once attackers obtain a recovery phrase, they can potentially access the cryptocurrency wallet from anywhere.

The biggest lesson is that purchasing from an authorised reseller does not automatically eliminate supply-chain risks.


4. Sentiment and Impact Ratings

My assessment uses a 1–10 scale, where 10 represents the highest negative sentiment or potential impact.

CategoryRatingAssessment
Negative sentiment8/10Significant concerns about hardware wallet security
Cybersecurity impact9/10Demonstrates sophisticated physical supply-chain attacks
Cryptocurrency industry impact8/10Could undermine confidence in hardware wallet manufacturers
Singapore impact8/10Relevant following the local Ledger incidents
Social media virality5/10Strong specialist interest but limited mainstream discussion
Long-term industry impact8/10Could accelerate supply-chain verification and security improvements

Overall Ratings

Sentiment: 8/10 (Strongly Negative)

The incident creates negative sentiment because cryptocurrency investors traditionally purchase hardware wallets to protect their assets.

Discovering that genuine hardware wallets can contain hidden malicious components challenges that confidence.

Impact: 9/10 (Very High)

The impact is potentially substantial because:

  • It affects trust in hardware wallet manufacturers.
  • It demonstrates that authorised distribution channels can be compromised.
  • It follows similar incidents involving Ledger.
  • It could encourage manufacturers to strengthen supply-chain verification.
  • It highlights the limitations of relying solely on firmware security.

However, the confirmed scope remains relatively small: three Trezor devices, with no reported financial losses.


5. My Overall Assessment

I would classify this as a high-impact cryptocurrency cybersecurity story rather than a widespread cryptocurrency market event.

Three things stand out:

1. The attack is unusually sophisticated.

Instead of compromising software, attackers physically modified genuine hardware wallets. The hidden cellular component could silently capture recovery phrases.

2. The problem extends beyond Trezor.

The connection to the earlier Ledger incident involving CryptoBilis makes this more concerning. It suggests that the supply chain itself deserves greater scrutiny.

3. Singapore has a reason to pay attention.

With the earlier Singapore Police Force advisory involving Ledger devices, local cryptocurrency investors should be particularly aware of this development.

Final Scorecard

MeasurementScore
Negative sentiment8/10
Overall impact9/10
Public interest6/10
Singapore relevance8/10
Potential long-term consequences8/10

Verdict: 8.5/10 – High significance.
Friday, 2 October 2026

Crypto Updates: Singapore crypto activity grows 55% as broader region contracts


Source:


ChatGPT:


πŸ‡ΈπŸ‡¬ Crypto in Singapore: what the article is really saying

The Cointelegraph article reports that Singapore's crypto activity reached US$284 billion (about S$370 billion) in the 12 months to June 2026, up 55.4% year-on-year. The striking part is that this happened while the broader Central & Southeast Asia and Oceania (CSAO) crypto economy contracted 6.8%. (Cointelegraph)

The headline numbers

MetricSingapore
Crypto activityUS$284B
YoY growth+55.4%
Institutional-platform activityUS$60B
Institutional growth+94%
Regional crypto economy-6.8%
Singapore's positionLargest measured crypto economy in CSAO

The US$284B figure is transaction/activity volume, not US$284B of crypto assets owned by Singaporeans. This distinction is important: it covers estimated crypto transaction flows associated with Singapore, rather than wealth/AUM sitting in Singapore. (Chainalysis)


🏦 The really important story: institutions

The biggest driver wasn't ordinary Singaporeans suddenly buying Bitcoin.

Institutional-platform activity jumped 94% to US$60 billion.

Chainalysis says this activity was concentrated among a relatively small number of:

  • market makers

  • OTC trading firms

  • institutional brokerages

  • existing platforms

And this is an important qualification:

Singapore's growth was not primarily the result of lots of new crypto businesses entering the market.

Chainalysis describes it as predominantly higher-volume activity from existing platforms. (Cointelegraph)

That makes the headline “Singapore crypto boom” somewhat misleading if interpreted as mass retail adoption.

It is more accurately:

Singapore is becoming a bigger institutional digital-asset trading/financial-services centre.


πŸ‡ΈπŸ‡¬ This fits Singapore's regulatory strategy

The interesting contradiction is that Singapore has simultaneously been tightening crypto regulation.

In 2025, MAS required Singapore-based crypto firms serving overseas customers to obtain a licence or exit that business. That reduced some speculative activity, according to StraitsX CEO Tianwei Liu, while leaving larger institutional players and companies using blockchain in production. (Cointelegraph)

At the same time, Singapore is pushing:

  • tokenisation

  • regulated stablecoins

  • digital-asset settlement

  • blockchain-based financial infrastructure

For example, MAS's BLOOM programme is testing regulated stablecoins and tokenised bank money, while Ripple joined a pilot involving cross-border trade settlement using RLUSD. (Cointelegraph)

So the broader strategy appears to be:

Less speculative crypto casino → more regulated institutional digital assets.

That's arguably the most important takeaway from the article.


🌏 Singapore vs the rest of Southeast Asia

The regional picture is fascinating.

Singapore is becoming more institutional, while the Philippines, Thailand and Vietnam are seeing much more small-value/P2P usage.

Those three countries recorded 5.4 million P2P transfers below US$10,000, representing 14.4% of global transfers in that category, despite accounting for only 2.5% of the global crypto economy. (Cointelegraph)

And stablecoins are becoming particularly important for cross-border transactions.

Chainalysis says cross-border stablecoin activity was 3.2 times domestic activity across the region. (Cointelegraph)

This makes sense for countries with:

  • large migrant-worker populations

  • remittances

  • expensive/slow traditional international transfers

  • weaker local currency liquidity


πŸ’¬ What is social media saying?

This article is very new, so the social-media footprint is still relatively small.

I found the strongest directly searchable discussion on Reddit, plus older HardwareZone discussions that provide useful Singapore context. Search indexing for X, Facebook, Instagram, TikTok and Threads is much poorer, so I wouldn't claim that the available results represent those platforms statistically.

Reddit

The initial Reddit discussion is relatively small — one direct repost currently has only a handful of votes — but the reaction is broadly positive toward Singapore's institutional crypto position. (Reddit)

The interesting point is that crypto-focused communities tend to interpret the US$284B figure as evidence that Singapore is becoming a serious institutional crypto hub.

However, there's an important caveat that comes through when comparing the Chainalysis report with the article:

US$284B doesn't mean Singapore residents suddenly became US$284B richer in crypto.

It represents measured transaction activity.

That's a distinction that could easily get lost in social-media headlines.


HardwareZone πŸ‡ΈπŸ‡¬

I couldn't find a significant new HWZ thread specifically discussing this September 2026 Chainalysis number.

But an older HWZ discussion is highly relevant because Singapore's crypto policy has long been framed as:

Singapore wants blockchain/financial innovation, but not uncontrolled speculative crypto trading.

That theme appeared explicitly in a 2022 HardwareZone discussion about MAS's approach. (HardwareZone Forums)

That makes the new data quite interesting.

What MAS has been trying to build appears increasingly visible in the numbers:

institutional blockchain/crypto infrastructure rather than mass speculative retail trading.


πŸ“± X / Facebook / Instagram / TikTok / Threads

The current indexed results don't provide enough direct, reliable posts from these platforms to claim a representative sentiment measurement.

The themes being circulated are nevertheless fairly predictable:

🟒 Positive

  • “Singapore is becoming Asia's crypto hub.”

  • Institutional money is coming in.

  • Regulation isn't killing crypto in Singapore.

  • Tokenisation and stablecoins could become mainstream financial infrastructure.

  • Singapore is outperforming the broader region.

🟑 More cautious

  • US$284B is transaction volume, not assets under management.

  • Much of the increase is concentrated in a small number of institutional platforms.

  • This doesn't necessarily mean ordinary Singaporeans are embracing crypto.

  • Singapore's tighter rules could push some crypto companies toward Hong Kong/Dubai.

That last point is particularly relevant because the Financial Times previously reported that MAS's crackdown on overseas-focused crypto businesses was expected to encourage some firms to move activity toward Hong Kong and Dubai. (Financial Times)


⚠️ The biggest misconception to avoid

If you're thinking of turning this into a YOLOFOMO101 post, don't write:

“Singaporeans now have a $284 billion crypto economy.”

That's misleading.

A much more accurate interpretation is:

“Singapore recorded US$284 billion of crypto activity over the year, with institutional platforms accounting for US$60 billion.”

The distinction between transaction volume, assets under management and wealth owned by residents is crucial.


πŸ“Š Sentiment & impact

I'd score it like this:

MeasureScore
Positive sentiment7/10
Negative sentiment3/10
Overall sentiment7/10
Social-media discussion5/10
Singapore relevance9/10
Financial-industry relevance9/10
Crypto-industry relevance9/10
Immediate consumer impact4/10
Long-term significance8/10
Overall article impact8/10

⭐ My overall rating: 8/10 impact

The sentiment is relatively positive, but the impact is much higher than the social-media noise currently suggests.

Why?

Because the US$284B number provides evidence of something strategically important:

Singapore's crypto story may be shifting from “retail speculation” toward institutional digital-asset infrastructure.

And that aligns quite closely with MAS's broader direction on tokenisation, stablecoins and regulated digital-asset settlement. (Chainalysis)


πŸ”₯ The best angle for your blog

For YOLOFOMO101, I wouldn't make the story simply:

“Singapore's crypto economy hits US$284 billion!”

That's basically repeating Cointelegraph.

A stronger angle would be:

“Singapore's crypto economy just hit US$284B — but Singaporeans aren't necessarily buying US$284B of Bitcoin.”

Then explain the surprising bit:

US$284B activity → +55.4%
Institutional activity → +94% / US$60B
Region overall → -6.8%

And the punchline:

Singapore isn't necessarily becoming a nation of crypto punters. It's increasingly becoming a place where institutions trade, settle and tokenise digital assets.

That is much more interesting for a Singapore audience — and it also connects nicely with the broader themes you've covered around MAS, fintech, tokenisation, stablecoins and the Singapore-vs-Hong Kong financial hub competition.

Sunday, 13 September 2026

Investing Updates: Gemini receives Singapore payment license for crypto services


Source:


ChatGPT:


Here’s a Singapore-focused summary of the Cointelegraph article, with a check of the available discussion across HardwareZone, Reddit and social platforms.

πŸ“° What happened?

Cointelegraph — Gemini receives Singapore payment license for crypto services

Gemini has officially received a Major Payment Institution (MPI) licence from the Monetary Authority of Singapore (MAS) through its local entity, Gemini Digital Payments Singapore.

This is significant because Gemini had only held in-principle approval (IPA) since October 2024. The final licence therefore took roughly 23 months to obtain. (Cointelegraph)

The licence allows Gemini Singapore to provide:

  • Digital Payment Token (DPT) services

  • Cross-border money-transfer services

  • Spot crypto trading

  • Digital-asset custody

  • OTC services

Gemini has been serving Singapore customers since 2020. In April 2025, it moved Singapore customers from its US entity, Gemini Trust Company, to its locally incorporated Singapore entity while awaiting the full licence. (Cointelegraph)

Why the MPI licence matters

The biggest practical difference is scale.

An MPI licence isn't subject to the transaction-volume ceilings applicable to a Standard Payment Institution. That gives Gemini much more room to grow its Singapore business, particularly for institutional clients. In exchange, MPIs face more extensive regulatory requirements because of their larger potential scale and risk. (Cointelegraph)

So this isn't really a new "Gemini is now allowed to operate crypto in Singapore" story. Gemini was already operating here.

It's more accurately:

Gemini has now completed the transition from operating under its previous exemption/IPA arrangements to being fully licensed by MAS.

Gemini itself says Singapore is a strategic hub for both its retail and institutional business in APAC. (Gemini)


πŸ‡ΈπŸ‡¬ What Singapore crypto users are saying

The interesting part is that the immediate online reaction appears relatively muted compared with the importance of the regulatory milestone.

HardwareZone

I couldn't find a substantial new HWZ thread specifically discussing the September 2026 Gemini licence announcement.

However, HWZ's long-running cryptocurrency discussions give some useful context.

In the Cryptocurrency Platforms Thread, users previously cited Gemini's advantages as relatively low fees on ActiveTrader, SGD deposits and withdrawals, and reasonable convenience. At the same time, some users expressed concerns about Gemini's liquidity and account/withdrawal experiences. (HardwareZone Forums)

The much larger Crypto Currency Chit Chat Group shows a similar split. Some users reported very fast Gemini withdrawals, while others said they were uncomfortable with Gemini because of reports of accounts being locked on Reddit. (HardwareZone Forums)

That tells me the Singapore crypto community's attitude isn't simply:

"MAS licence = Gemini is now great."

It is more:

"Regulation is a positive, but users still care about fees, liquidity, withdrawals and whether the exchange is actually reliable."

That's particularly relevant after the Tokenize Xchange problems in Singapore. HWZ discussions around Tokenize highlighted how an exchange operating under an exemption isn't necessarily MAS-licensed or protected by the same regulatory safeguards. (HardwareZone Forums)


Reddit sentiment

Reddit discussion specifically about the new September 2026 licence is still quite limited because the announcement is only a few days old.

There is, however, an interesting historical comparison.

When Gemini announced its in-principle approval in 2024, some Reddit users were sceptical about Gemini's customer-service and account-freezing experiences. One user claimed their account had been frozen for weeks, while another described withdrawal problems. (Reddit)

That doesn't mean those complaints represent Gemini's current Singapore service, but they show an important theme in the community:

Regulatory approval doesn't automatically eliminate concerns about the exchange's operational/customer-service experience.

There is also considerable Singapore Reddit discussion around the importance of using properly licensed exchanges, particularly following the Tokenize episode. (Reddit)


πŸ“± X / Facebook / Instagram / TikTok / Threads

I found much less substantive public discussion on these platforms than the amount of promotional/industry sharing around the announcement.

The strongest visible reaction is from the crypto/fintech professional community, rather than ordinary Singapore retail investors.

For example, Gemini's Singapore announcement is being amplified by people in the Singapore fintech/legal ecosystem, with posts congratulating Gemini and highlighting the company's retail and institutional ambitions. (LinkedIn)

I wouldn't characterise the current social-media reaction as a huge consumer conversation. The announcement appears to be getting more attention from crypto-industry professionals than from everyday Singapore investors.

That's actually quite telling.


πŸ’‘ My take: Why this matters

I'd rate this as more strategically important than immediately useful to retail users.

1. It's a credibility boost

Having MAS formally licence Gemini gives Singapore users another major globally recognised exchange operating under the local regulatory framework.

That's increasingly important after the failures/problems surrounding offshore and lightly regulated crypto platforms.

2. It gives Gemini room to grow

The removal of transaction-volume restrictions is arguably the biggest business benefit.

Gemini can now pursue larger institutional flows, rather than treating Singapore mainly as a regional retail market. Gemini explicitly describes Singapore as a hub for retail and institutional customers. (Gemini)

3. But don't confuse "MAS licensed" with "MAS guarantees your money"

This is probably the most important point for Singapore investors.

An MPI licence means Gemini is authorised and subject to MAS regulatory requirements. It does not mean MAS guarantees the value of your crypto or eliminates exchange/custody risks.

The distinction is particularly relevant given the experiences of Singapore users with crypto platforms that subsequently ran into trouble. (HardwareZone Forums)

4. Gemini's biggest challenge is now competition

Gemini isn't entering an empty market.

Singapore users already have various regulated/locally accessible options, including Coinbase, Crypto.com, Independent Reserve, Coinhako and others. HWZ discussions show users already comparing exchanges primarily on fees, SGD funding, liquidity, withdrawal speed and available coins, rather than simply whether an exchange is licensed. (HardwareZone Forums)

So Gemini's licence removes one major disadvantage — regulatory uncertainty — but doesn't automatically make it the best exchange.


🧾 Bottom line

The article is essentially good news for Gemini, but not a game-changing development for existing Singapore retail users.

AreaImpact
MAS regulatory status🟒 Major positive
Gemini credibility in SG🟒 Positive
Institutional expansion🟒 Very positive
Transaction capacity🟒 Major improvement
New retail features🟑 None announced yet
Fees🟑 No immediate change
Crypto investment riskπŸ”΄ Still exists
Competitive position🟑 Better, but crowded
Social-media reaction🟑 Relatively muted

The bigger story is not "Gemini gets a licence." It's that Singapore continues to position itself as a regulated crypto hub, while increasingly forcing exchanges to move from temporary exemptions/looser arrangements into formal MAS supervision.

For a Singapore crypto user, I'd therefore interpret this as "Gemini has become a more legitimate/established local exchange option" rather than "Gemini is now necessarily the best place to buy crypto." (Cointelegraph)

Friday, 14 August 2026

Crypto Updates: Trezor Customer Data Exposed in Shipping Partner Breach


Source:


ChatGPT:


A data breach at ShipMonk, a third-party fulfilment partner used by Trezor, exposed personal information belonging to 13,689 Trezor customers. The incident affected customers who ordered between May 10 and August 8, 2026, across the US, UK, Sweden, Colombia, Brazil, Italy and Portugal. (Decrypt)

Of those affected, 11,742 customers had their full names, shipping addresses, phone numbers and email addresses exposed, while another 1,947 had their names, cities and email addresses leaked. Trezor says its own systems were not compromised and that wallets, private keys, recovery backups and devices remain secure. (Protos)

The bigger concern is what criminals can do with the information. Because the victims can now potentially be identified as Trezor customers—and, for most, their home addresses are known—the data could enable highly convincing phishing, impersonation and social-engineering attacks. The article also highlights the more serious possibility of physical targeting, noting that crypto-related “wrench attacks” have been increasing. (CryptoRank)

Trezor says its policy requiring fulfilment partners to delete or anonymise order data after 90 days limited the breach's scale. It is also accelerating an Anonymous Delivery option involving locker collection, neutral packaging, generic sender information and automatic deletion of shipping identifiers. The service is targeted for the EU by September and the US by year-end.

The incident comes shortly after the major Coldcard security crisis, making hardware-wallet users particularly nervous. However, the two incidents are fundamentally different: Trezor itself was not hacked, whereas the ShipMonk breach exposed customer information held by a logistics provider.

The main lesson is that even when a hardware wallet securely protects cryptocurrency, the purchase trail and customer's physical identity can remain a significant security vulnerability.

Social media & forum reaction

Reddit has the clearest and strongest reaction so far. A post in r/Bitcoin received about 310 upvotes, while Trezor's own Reddit announcement received about 308. (Reddit)

The dominant sentiment is essentially: “The wallet is safe, but the owner is now easier to target.”

One particularly useful Reddit discussion distinguishes the breach from an actual wallet hack: users emphasised that attackers did not obtain seed phrases, private keys or wallet access. (Reddit)

However, anxiety is still substantial. Users specifically worry about:

  • Targeted phishing using their real name and purchase history.

  • Criminals knowing their home address.

  • Potential physical attacks against wealthy crypto holders.

  • Trezor's reputation after Ledger previously suffered a customer-data breach.

  • Whether moving to another hardware-wallet manufacturer actually solves the underlying supply-chain/privacy problem. (Reddit)

There is also frustration from customers who recently bought Trezor specifically because of the recent Coldcard incident. Some commenters described the timing as particularly unfortunate, while others stressed that ShipMonk—not Trezor's wallet infrastructure—was breached. (Reddit)

Interestingly, users are also discussing Amazon purchases. Trezor representatives confirmed that orders from its official Amazon stores use a different fulfilment partner and were not affected. (Reddit)

r/CryptoCurrency reflects similar concerns, with users noting that the Coldcard incident may have pushed more people towards Trezor shortly before this breach. (Reddit)

HardwareZone: I couldn't find a meaningful current HardwareZone discussion specifically about this breach, so there isn't enough evidence to claim a Singapore-forum consensus.

X, Facebook, Instagram, TikTok and Threads: Publicly searchable discussion remains limited because posts are frequently login-gated or poorly indexed. I therefore wouldn't assign a sentiment percentage to these platforms.

Overall takeaway

This is not a Trezor wallet-security breach. It is a customer-privacy and physical-security breach—and arguably that distinction is the most important point.

For affected users, the realistic immediate threat is much more sophisticated phishing, not someone remotely emptying the Trezor. But because the leaked information can link a person's identity and home address to ownership of a hardware wallet, the incident is considerably more serious than an ordinary email database leak. (Financial Times)

Friday, 7 August 2026

Crypto Updates: Coldcard Bitcoin Exploit Explained: Entropy, How Keys Are Generated, and Why Bits Matter


Source:


ChatGPT:


Decrypt explains how a Coldcard firmware bug turned Bitcoin wallets into predictable targets, with losses exceeding US$100 million and potentially reaching US$130 million. Galaxy Research has identified 1,596 BTC stolen across three attack waves, while a suspected fourth wave could raise the total to 2,055 BTC. At least 15 attackers are reportedly exploiting the vulnerability.

The problem began after a 2021 cryptography-library migration. A build-configuration mistake caused Coldcard seed generation to bypass its hardware random-number generator and instead use MicroPython’s Yasmarang pseudo-random generator. On older Mk2 and Mk3 devices, resulting seeds had only 40 bits of effective entropy, compared with the intended 128 bits. Newer models mixed in additional secure-element entropy but still fell short, at roughly 72 bits.

Entropy measures how unpredictable a secret is: each bit doubles the attacker’s search space. A 128-bit seed is effectively impossible to brute-force, while 40 bits represents roughly one trillion possibilities—small enough for computers to search.

The incident has also reignited debate over physical dice as an alternative entropy source. Coldcard recommends at least 50 dice rolls for 128-bit security and 99 for 256-bit security. Bitcoin Core developer Luke Dashjr warned that ordinary dice are imperfect, prompting online debate over whether casino dice are necessary. Critics noted that minor dice bias costs only a few bits, vastly less than Coldcard’s entropy failure.

The key lesson is that statistical randomness is not enough; cryptographic randomness must be unpredictable. Updating firmware does not repair compromised seeds. Affected users must generate a new seed and move their funds. The breach also highlights risks of relying on one security component, even in open-source, audited hardware wallets.

Social media & forum reaction

The story has generated substantial discussion in Bitcoin communities, particularly Reddit and X. The reaction is much more technical—and much more emotional—than a normal hardware-wallet product controversy.

πŸ”΄ Reddit: trust in Coldcard has taken a major hit

The strongest reaction is from actual Coldcard users. One user who moved away from Coldcard despite using an Mk4 with dice and a passphrase wrote that the incident had “humbled a lot of people” who believed they were using one of the safest forms of self-custody. (Reddit)

Another particularly painful Reddit post came from a user who said they had lost 1 BTC, accumulated through years of dollar-cost averaging. The emotional response highlights why this incident is damaging to Coldcard's reputation beyond the technical vulnerability itself. (Reddit)

There is also a counter-camp arguing that the vulnerability should not be interpreted as “all Coldcards are unsafe.” Users who generated seeds through the dice-roll method generally argue that their seeds were not affected, while others say they are still migrating because they no longer trust the manufacturer. (Reddit)

🎲 The “you can't even trust dice?” debate

This has become one of the most entertaining parts of the discussion.

Luke Dashjr's warning that ordinary dice aren't cryptographically perfect triggered jokes and criticism. The debate is essentially:

Technical position: casino-grade dice have measurable manufacturing bias.

Practical position: a slightly biased die is nowhere near as dangerous as Coldcard's reduction from 128-bit security to roughly 40 bits.

That distinction is important. Coldcard itself says each D6 roll contributes about 2.585 bits, requiring at least 50 rolls for 128-bit security and 99 for 256-bit security. (COLDCARD)

Reddit users are consequently debating whether the bigger lesson is “use better dice” or “don't trust a single entropy source.” (Reddit)

πŸ”₯ Self-custody debate

Another major discussion is whether the incident proves that Bitcoin self-custody itself is flawed.

The answer from many Bitcoin users is emphatically no. One Reddit discussion argues that the failure was specifically a Coldcard implementation problem rather than a failure of Bitcoin or self-custody. (Reddit)

Others are now advocating:

  • Multisig using different manufacturers

  • Independently generated entropy

  • Dice-generated seeds

  • Passphrases

  • More rigorous third-party testing

  • Multiple independent entropy sources

A particularly interesting Reddit discussion argues that multisig across different vendors may be the better long-term answer because it reduces dependence on one company's firmware. (Reddit)

𝕏 X / Bitcoin Twitter

X discussion has focused heavily on the dice controversy, the tiny #ifndef coding mistake, AI-assisted code review and whether Coldcard can regain trust.

The article's quoted exchanges capture the mood: some users joked that “now you can't even roll dice,” while developers countered with calculations showing that modest dice bias would cost only a few entropy bits—not the enormous security reduction caused by the Coldcard bug.

There is also considerable criticism of the idea that open-source automatically means secure. The uncomfortable lesson is that Coldcard's code was available for inspection for years, yet the critical path was not adequately tested.

Galaxy's latest investigation adds another layer: confirmed losses have risen to 1,596 BTC from about 7,300 addresses, with the suspected fourth wave potentially taking the total to 2,055 BTC. (crypto.news)

🟑 HardwareZone

I couldn't find a substantial, publicly indexed Singapore HardwareZone thread specifically discussing this August 2026 Coldcard exploit. That is notable because the incident is currently being discussed much more heavily in global Bitcoin communities than Singapore's mainstream tech forums.

Facebook, Instagram, TikTok & Threads

Likewise, I couldn't find enough publicly indexed posts on Facebook, Instagram, TikTok or Threads to establish a reliable platform-wide sentiment specifically about this incident. I would avoid treating isolated reposts or algorithmically surfaced videos as representative.

Overall sentiment

πŸ”΄ Negative toward Coldcard, but not necessarily negative toward Bitcoin.

The dominant themes are:

1. Loss of trust: Users are questioning whether Coldcard deserves its previous reputation as one of the safest Bitcoin hardware wallets.

2. “Open source isn't enough”: The incident demonstrates that publicly available code can still contain catastrophic bugs.

3. Entropy is now the star of the conversation: Users are suddenly discussing randomness, dice, RNGs and bits—topics normally invisible to everyday Bitcoin holders.

4. Self-custody survives, but practices may change: Multisig, independent entropy and multiple vendors are receiving renewed attention.

5. AI creates an uncomfortable twist: Coinkite suspects AI-assisted code analysis may have helped attackers find the vulnerability, while its own AI review reportedly missed it. This remains an attribution claim, not a proven explanation of how the attackers discovered the flaw.

The biggest takeaway from the online discussion is therefore not “hardware wallets are unsafe.” It is closer to: “Don't confuse a secure-looking device with a secure key-generation process.” The incident demonstrates why entropy generation is arguably the single most important part of a hardware wallet's security model. (COLDCARD)

Saturday, 25 July 2026

Investing Updates: Fears of AI-driven DeFi hack epidemic overstated for now — but not for long

Source:

https://cointelegraph.com/magazine/ai-hasnt-unleashed-a-defi-hackpocalypse-but-its-making-every-weakness-more-dangerous

ChatGPT:

Concerns about an AI-driven wave of decentralized finance (DeFi) hacks have grown following several major crypto exploits in 2026, but security experts argue the threat is real yet still emerging rather than already causing a full-scale crisis. After approximately $630 million in losses during April, some industry figures warned that AI could rapidly identify smart contract vulnerabilities, making all DeFi protocols vulnerable. However, subsequent data suggests fears of an immediate "hackpocalypse" may have been exaggerated. (The New York Ledger)

According to CertiK, over $1.3 billion was lost across 344 Web3 security incidents during the first half of 2026. While it is difficult to prove AI directly discovered vulnerabilities, researchers observed a sharp rise in attacks against older and unverified smart contracts, suggesting AI is helping attackers analyze much larger codebases more efficiently. Rather than creating entirely new attack methods, AI is making existing exploits faster, cheaper and easier to scale. (The New York Ledger)

Chainalysis also found AI-enabled crypto scams are significantly more profitable than traditional scams, aided by deepfakes, impersonation attacks and automated phishing campaigns. AI lowers the technical barrier for cybercriminals, allowing them to target more victims simultaneously. (The New York Ledger)

Despite these developments, compromised private keys, poor operational security and infrastructure failures remain the primary causes of major crypto thefts. Hacken estimates nearly 88% of stolen funds during Q2 2026 resulted from compromised credentials rather than smart contract bugs. Recent exploits, including AFX Trade and other bridge attacks, reinforce that off-chain security remains the weakest link. (CoinDesk)

Experts conclude AI is becoming a powerful force multiplier for both attackers and defenders. Organizations that successfully deploy AI-powered security monitoring, code auditing and fraud detection are expected to gain a significant defensive advantage as AI capabilities continue to improve. (The New York Ledger)


Social media and forum discussions

Reddit

Discussion across r/CryptoCurrency, r/ethfinance, r/DeFiSecurity and other crypto communities generally agrees that AI has not yet caused a DeFi security apocalypse, but many believe it is accelerating vulnerability discovery.

Common themes include:

  • AI is helping hackers audit thousands of smart contracts much faster.

  • Most recent high-profile hacks still originated from stolen private keys, phishing or poor operational security rather than AI-generated exploits.

  • Developers are increasingly using AI for automated smart contract reviews and bug hunting, creating an "AI vs AI" security race.

  • Several users argue protocol governance and infrastructure remain bigger risks than AI itself. (GummySearch)

X (formerly Twitter)

Crypto security researchers including CertiK, PeckShield, Blockaid and SlowMist have been actively discussing:

  • AI-assisted vulnerability discovery.

  • Rising phishing attacks using AI-generated content.

  • Calls for stronger operational security instead of focusing solely on smart contract audits.

  • Debate over whether recent hacks truly involved AI or simply exploited existing weaknesses. (CoinDesk)

HardwareZone (Singapore)

No meaningful discussion thread specifically about this article or AI-driven DeFi hacking was found. Most cryptocurrency conversations remain focused on Bitcoin prices, exchange regulation and investment strategies rather than AI-assisted security threats. (The New York Ledger)

Facebook

Crypto security companies and blockchain news pages shared the article and related reports. Comments largely emphasized:

  • Better wallet security.

  • Multi-signature wallets.

  • Hardware wallet adoption.

  • Skepticism that AI is the primary cause of recent losses.

Instagram

Crypto media accounts published infographic summaries highlighting:

  • "$1.3B lost in H1 2026."

  • AI making scams more convincing.

  • Tips on avoiding phishing and fake support accounts.

Engagement was moderate, with many users expressing concern about increasing sophistication of crypto scams.

TikTok

Crypto creators used the story to explain:

  • How AI can scan smart contracts.

  • AI-powered phishing and deepfake scams.

  • Why hardware wallets and cold storage remain important.

Videos generally portrayed AI as an amplifier rather than an entirely new hacking method.

Threads

Discussion mirrored X, with developers and investors debating:

  • Whether AI is overhyped as a security threat.

  • The importance of improving key management and governance.

  • Expectations that AI-assisted attacks will become more common over the next few years.

Overall sentiment

The consensus across industry experts and online communities is cautiously balanced. Most agree that AI has not yet triggered widespread automated DeFi exploits, but it is rapidly lowering the cost and speed of cyberattacks. The immediate priority remains strengthening private key management, infrastructure security and operational practices, while preparing for increasingly capable AI-assisted attackers in the near future. (The New York Ledger)

Saturday, 11 July 2026

Crypto Updates: Ledger researchers disclose Tangem card flaw; Tangem says risk to everyday users is 'virtually non-existent'


Source:


ChatGPT:


Ledger's security research team, Ledger Donjon, disclosed a hardware vulnerability affecting all Tangem hardware wallet cards currently in circulation. The flaw allows an attacker to reset a Tangem card's password through a sophisticated laser fault injection attack, potentially enabling unauthorized access to crypto assets stored on the wallet. (Ledger Donjon)

The attack exploits a weakness in Tangem's firmware running on an EAL6+ secure element. By exposing the chip, attaching custom hardware and firing a precisely timed nanosecond laser pulse at a specific location, researchers bypassed a firmware check that normally verifies whether the card is in recovery mode. This allowed them to assign a new password without knowing the original password or possessing a backup card. Once completed, the attacker could sign transactions and transfer cryptocurrency. (Ledger Donjon)

Ledger Donjon stressed that the attack is highly impractical for ordinary criminals. It requires physical possession of the card, invasive modification that permanently damages the device, roughly US$250,000 worth of laboratory equipment, side-channel analysis tools and advanced hardware security expertise. Researchers successfully repeated the attack on multiple cards, with each exploit taking around two hours once the process had been established. Since Tangem cards cannot receive firmware updates, the vulnerability cannot be patched through software. (Ledger Donjon)

Tangem disputed the practical significance of the findings, arguing the risk to everyday users is "virtually non-existent." The company noted that Ledger Donjon operates within competitor Ledger and said similar attacks could eventually be developed against any secure element given sufficient resources. Tangem maintains that users who keep their cards secure are unlikely to face any realistic threat, although Ledger advises that lost or stolen cards present the primary risk scenario. (Ledger Donjon)

Social media and forum discussions

Reddit

  • Most discussion occurred in r/Tangem and r/ledgerwallet.

  • Opinion was divided:

    • Some viewed the disclosure as a legitimate hardware vulnerability because it has been demonstrated repeatedly.

    • Others argued the attack is unrealistic due to the US$250,000 lab setup and physical access requirements.

    • Several users questioned whether Tangem should offer upgraded cards despite the low practical risk. (Reddit)

HardwareZone

  • No significant discussion thread was found as of 11 July 2026.

X (Twitter)

  • Crypto security accounts widely shared the research.

  • Debate centred on whether the issue represents a serious security flaw or an academic proof-of-concept.

  • Some criticised Tangem's lack of firmware updates, while others defended the product because the attack cannot be performed remotely. (Ledger Donjon)

Facebook

  • Limited discussion, mostly news reposts with comments advising users not to lose their hardware wallets.

Instagram

  • Crypto creators summarised the research, emphasising that physical possession is required and everyday users are unlikely to be targeted.

TikTok

  • Small number of crypto videos explained the "laser hack." Most concluded that although technically impressive, it poses little risk to average holders.

Threads

  • Users discussed whether immutable firmware is a security strength or weakness. Many said the inability to patch vulnerabilities is the more concerning aspect.

Overall sentiment

Sentiment is mixed but calm. Security researchers praised Ledger Donjon's technical achievement and transparency, while Tangem supporters argued the exploit has little real-world impact because it requires expensive equipment, specialist skills and physical possession of the wallet. The broad consensus is that users who keep their Tangem cards secure face minimal risk, but owners of high-value wallets should take extra care to prevent theft or loss.